
OUR BLOG
The EU just raised the bar on cybersecurity, and this time it’s not optional.
The NIS2 Directive (EU) 2022/2555 entered into force on January 16, 2023, and replaced the original NIS Directive. EU member states were required to transpose it into national law by 17 October 2024. If you operate in the EU, provide services to EU customers, or sit...
The Invisible Data Leak
You have firewalls, DLP, endpoint protection, and a 40-page data classification policy. Then an engineer pastes 2,000 lines of proprietary source code into a public LLM to debug it faster. A marketer uploads last quarter's unreleased financial forecast to summarize...
Why You Need a Cybersecurity Incident Response Team
It is no longer a question of whether your organisation will face a cybersecurity incident, but when. For years, security was sold as prevention. Firewalls, antivirus, awareness training. If we build high enough walls, the thinking went, we can keep the hackers out....
Mouse Jacking: The Wireless Exploit That Hackers Love
Mouse jacking a wireless exploit, which targets wireless mice and their receivers, allows hackers to take control of a computer or network without the victim’s knowledge. In this article, we will explore what mouse jacking is, how it works, and why it has become a...
Pentest Your Systems, Before Someone Else Does
In today’s increasingly connected digital world, cybersecurity has become more important than ever before. With businesses and organisations storing vast amounts of sensitive data online, from customer information to intellectual property, the risks associated with...
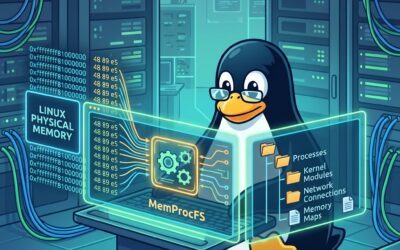
Teaching MemProcFS to Read Linux Memory
For years, [MemProcFS](https://github.com/ufrisk/memprocfs) has had one of the nicest workflows in memory forensics: point it at a memory image and it mounts the thing as a filesystem you can `cd` into, `cat`, and `grep` like a live machine. No query language to...